Control-M SSL Configuration
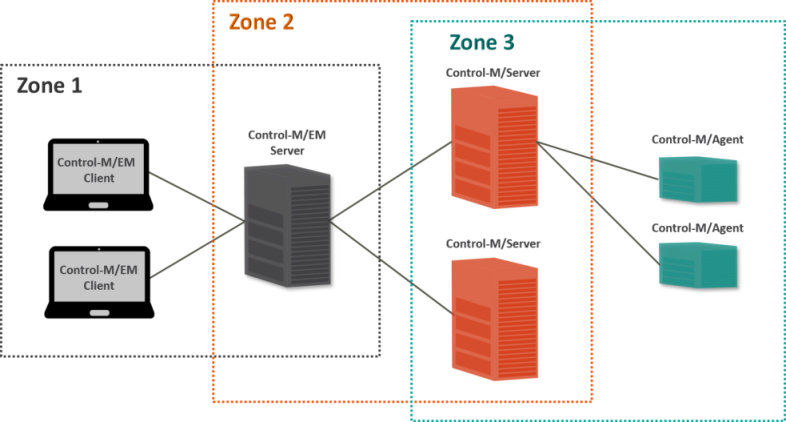
Control-M components can securely communicate via the SSL/TLS protocols and are categorized according to zones, as shown in the following diagram and description:
-
Zone 1: Encompasses communication between Control-M/EM clients (such as Control-M Web, Control-M Automation API, and utilities) and Control-M/EM servers, as described in Zone 1 SSL Configuration.
-
Zone 2: Encompasses communication between Control-M/EM servers and Control-M/Servers, as described in Zone 2 and 3 SSL Configuration.
-
Zone 3: Encompasses communication between Control-M/Servers and Agents, as described in Zone 2 and 3 SSL Configuration.
The following topics describe how you can configure SSL and security on these components:
-
LDAP SSL Configuration: Communication between Control-M/EM and the LDAP Server
-
Zone 1 SSL Configuration: Control-M Self Service and Control-M Workload Change Manager (WCM) security
-
Configuring Control-M MFT for an Alternative CA.: Control-M MFT security
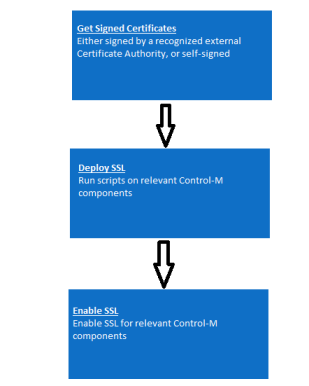
To configure SSL in your environment, you must do the following:
-
Get Signed Certificates: Signed certificates enable secure communication via SSL/TLS protocols. Control-M components support only PEM file types, which are ASCII-encoded X.509 certificates. By default, Control-M components and connected user interfaces are configured to communicate via SSL in new Control-M 9.0.27 installations. BMC recommends that you upload your own signed, organization-managed, SSL/TLS certificate that supports Control-M security level 4 when prompted during installation.
If you install Control-M with a less secure, automatically generated self-signed SSL certificate that only supports Control-M security level 2 (and is valid for 20 years), BMC recommends that you later replace this self-signed certificate with a signed, organization-managed SSL/TLS certificate that supports security level 4. You can do either of the following to get your certificates:
-
Get Certificates from Your Security Administrator: Obtain a PKCS#12 keystore
 A Public-Key Cryptography Standards (PKCS) #12 keystore is a password-protected, encrypted file that contains a private key, its matching SSL/TLS certificate, and optionally a certificate chain of intermediate and root Certificate Authority (CA) certificates. Control-M components use this keystore to authenticate each other and encrypt the data that they exchange over SSL/TLS, which protects workload data in transit and makes sure that each component connects only to trusted components. or a private key, signed certificate, and certificate of the root CA in PEM file format. This last file must also contain the certificate chain from the certificate that signed your certificate to the root CA certificate, if required.
-
Get Certificates with a CSR File: Obtain a signed certificate from a recognized CA using a Certificate Signing Request (CSR) file. If the server certificate is issued by an intermediate CA that has a certificate that is trusted by a root CA (whether directly or by a chain), you must obtain the certificate chain from the CA.
For more information, see Generating a Signed Certificate and Private Key, Generating a PKCS #12 Keystore, and Replacing Default Self-Signed Certificates with User-Provided Certificates at Security Level 4.
-
-
Deploy SSL: To create an SSL policy, you must deploy the PKCS#12 keystore to the relevant Control-M components, as described in Deploying a New Keystore in Zone 2 and 3.
-
Enable SSL: Enable SSL for relevant Control-M components.
 YouTube

 Facebook
 LinkedIn